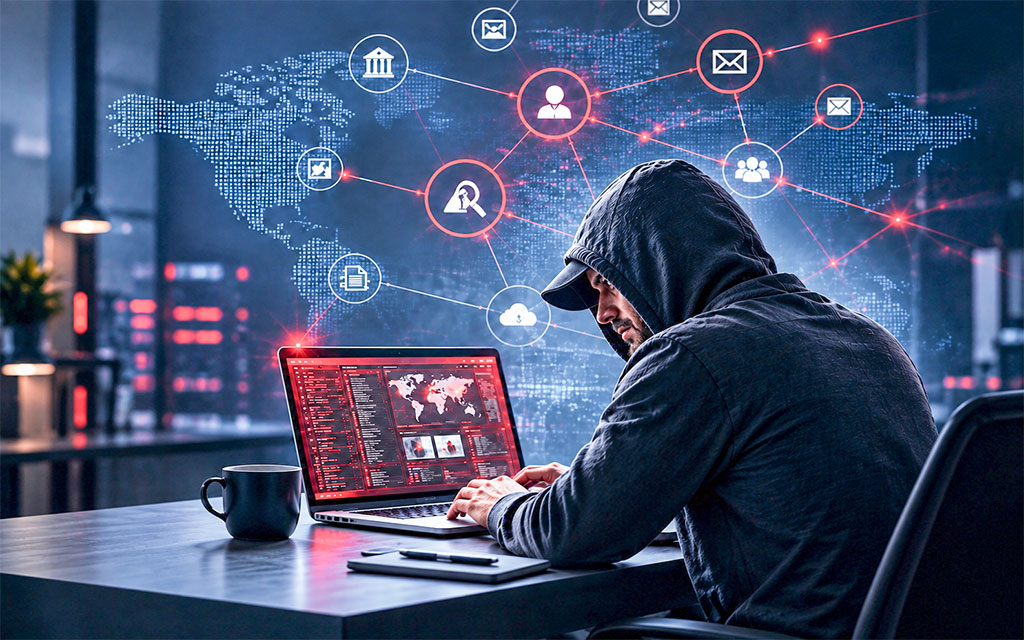
Ten years ago, a cybercriminal might have spent days researching a target. Today, AI can do much of that work in minutes.
The scary part isn't that AI can work faster. It's that it can uncover clues about your firm that you may not even realize are there.
AI can analyze information faster, connect dots humans might miss, and identify potential weaknesses in a fraction of the time. The result? Criminals can gather a surprising amount of intelligence about a business before they ever launch an attack.
Imagine giving a stranger access to your firm's digital footprint for just ten minutes.
What would they find?
For many firms, the answer is: more than you'd expect and far more than you would ever want to share.
The Information Is Already There
Cybercriminals don't have to spend hours scrolling through websites and piecing together clues anymore. AI does the heavy lifting, combing through everything from firm websites and LinkedIn profiles to old breach data and publicly available information at lightning speed.
That information can reveal:
- Who works at your firm
- Which vendors and software platforms you use
- Employee email formats
- Potential decision-makers
- Common business processes
- Valuable targets for phishing emails
Individually, these details may seem harmless. Together, they create a roadmap.
Small Clues Become Big Opportunities
One of the biggest advantages AI gives cybercriminals is the ability to connect information from multiple sources.
Maybe someone in accounting mentions a software migration on LinkedIn.
A manager posts photos from a firm event.
An employee uses the same password that was exposed in an old data breach.
None of these items seem particularly dangerous on their own.
But AI excels at spotting patterns, making connections, and identifying opportunities attackers can exploit.
Your Firm Is Encouraging AI. But Is It Being Used Safely?
Here's a question many law firms haven't stopped to ask:
If you're encouraging employees to use AI to be more productive, how do you know they're using AI safely?
Across the legal industry, firms are embracing AI-powered tools to draft emails, summarize documents, conduct research, create marketing content, and streamline administrative tasks. Productivity gains are real, and firms that ignore AI risk falling behind.
But many firms are pushing AI adoption before establishing clear policies around its use.
If your staff is using AI today, can you confidently answer these questions?
- Which AI platforms are employees using?
- Are they using firm-approved tools or personal AI accounts?
- Are client documents being uploaded into public AI platforms?
- Are confidential conversations being entered into AI systems?
- Is sensitive data being retained by third-party providers?
- Do employees understand what information should never be shared with AI?
For many firms, the honest answer is, "We're not sure."
That uncertainty creates risk.
Whether your firm uses cloud-based platforms like Clio, NetDocuments, and Microsoft 365, or relies on on-premises systems such as ProLaw and other legacy legal applications, employees are likely interacting with AI every day.
Without an AI Use Policy, every employee is making individual decisions about what tools to use, what data to share, and what risks are acceptable.
An effective AI Use Policy should address:
- Approved AI platforms
- Prohibited AI tools
- Client confidentiality requirements
- Data security standards
- Human review requirements
- Ethical and compliance considerations
- Acceptable use guidelines
Reality Check
If your firm is encouraging staff to "use AI to be more productive" but has not yet established an AI Use Policy, you're asking employees to make security and compliance decisions on their own.
AI can be a tremendous productivity tool, but productivity should never come at the expense of client confidentiality, ethical obligations, or cybersecurity.
The Scary Part Isn't What You Know About
Most firms spend time protecting what they know is important.
The bigger risk is often what they've forgotten.
Old user accounts.
Unused applications.
Shared folders with overly broad permissions.
Outdated recovery plans.
Files that have quietly accumulated sensitive information over the years.
And now, potentially, AI tools being used without oversight or security controls.
These hidden weaknesses are exactly the kinds of things criminals hope to discover first.
Would Your Firm Pass the Test?
If an AI-powered cybercriminal started investigating your firm right now, what would they learn in the first ten minutes?
More importantly, what would they find that could help them gain access, steal data, or disrupt your operations?
The same assessment should be applied internally:
What AI tools are being used inside your firm today? What information is being shared with them? And are adequate safeguards in place?
In our upcoming webinar, The Top 3 Things an AI-Powered Cybercriminal Will Find Inside Your Firm, we'll walk through the most common discoveries attackers make, how AI is changing the threat landscape, and what firms can do to reduce their exposure before those discoveries become costly problems.
You'll also learn why an AI Security & Usage Audit, combined with a comprehensive internal security assessment and penetration test, can help uncover risks before attackers do.
Register for the webinar and see what attackers see before they do. REGISTER HERE!